Two-factor authentication, usually shortened to 2FA, means signing in with two things instead of one: your password and a second check, such as a code from an app or a tap on a device you own. The point is simple. If someone steals your password, they still cannot get in without the second factor. This guide explains the mechanic in plain terms, then walks you through enabling 2FA on the accounts that matter most: email, banking, and social media.
Start with email. Your inbox is the master key to everything else, because password resets for other services arrive there. Banking comes next, then social accounts, then everything else as you find time. If you are completely new to this, you are in good company: as Vocabulary.com puts it, a beginner is someone who is brand new at something and still learning. That is all this guide assumes.
What is two factor authentication, exactly?
Think of the factors in three groups. Something you know, like a password. Something you have, like your phone or a security key. Something you are, like a fingerprint or your face. Two-factor authentication means a login needs a factor from two different groups. Password plus fingerprint counts. Password plus a second password does not.
The second factor exists to cover the main weakness of passwords: they get stolen. Phishing emails trick people into handing them over. Breaches leak them from company servers. People reuse them across sites. A stolen password alone then fails at login, because the attacker cannot produce the second factor.
One honest caveat before we go further. Not every second factor is equally strong. Codes sent by text message work, but they are the weakest common option, because phone numbers can be hijacked through attacks on mobile carriers. An authenticator app on your phone is stronger and works offline. A hardware security key, a small USB device, is the strongest option most people can buy. Start with whatever your account offers; upgrade later.
Which accounts should you protect first?
Work down this list in order. Each entry explains why it earns its rank.
- Email. Whoever controls your inbox can reset the password on almost every account you own. This is the single most important account to lock down.
- Banking and money. Your bank, brokerage, and any payment apps. Financial accounts are the direct target.
- Password manager. If you use one, it holds every other credential, so it needs its own second factor. If you do not use one yet, our guide on how to choose and set up a password manager in about an hour covers the setup.
- Social media. A hijacked account is used to scam your friends and contacts, often within minutes.
- Cloud storage and work accounts. These hold documents and files you cannot afford to lose or leak.
Everything else can wait a week. The top three usually take under an hour combined.
How do I turn on 2FA on my email account?
Menu paths shift as providers update their settings, so treat these as the general route and follow the on-screen labels if a screen looks different.
- Sign in on the web, not the mobile app. Settings are easier to navigate there.
- Open the account or security settings page. Look for words like Security, Sign-in, or Two-step verification.
- Choose the second-factor method. Pick Authenticator app if offered; otherwise Text message is fine to start.
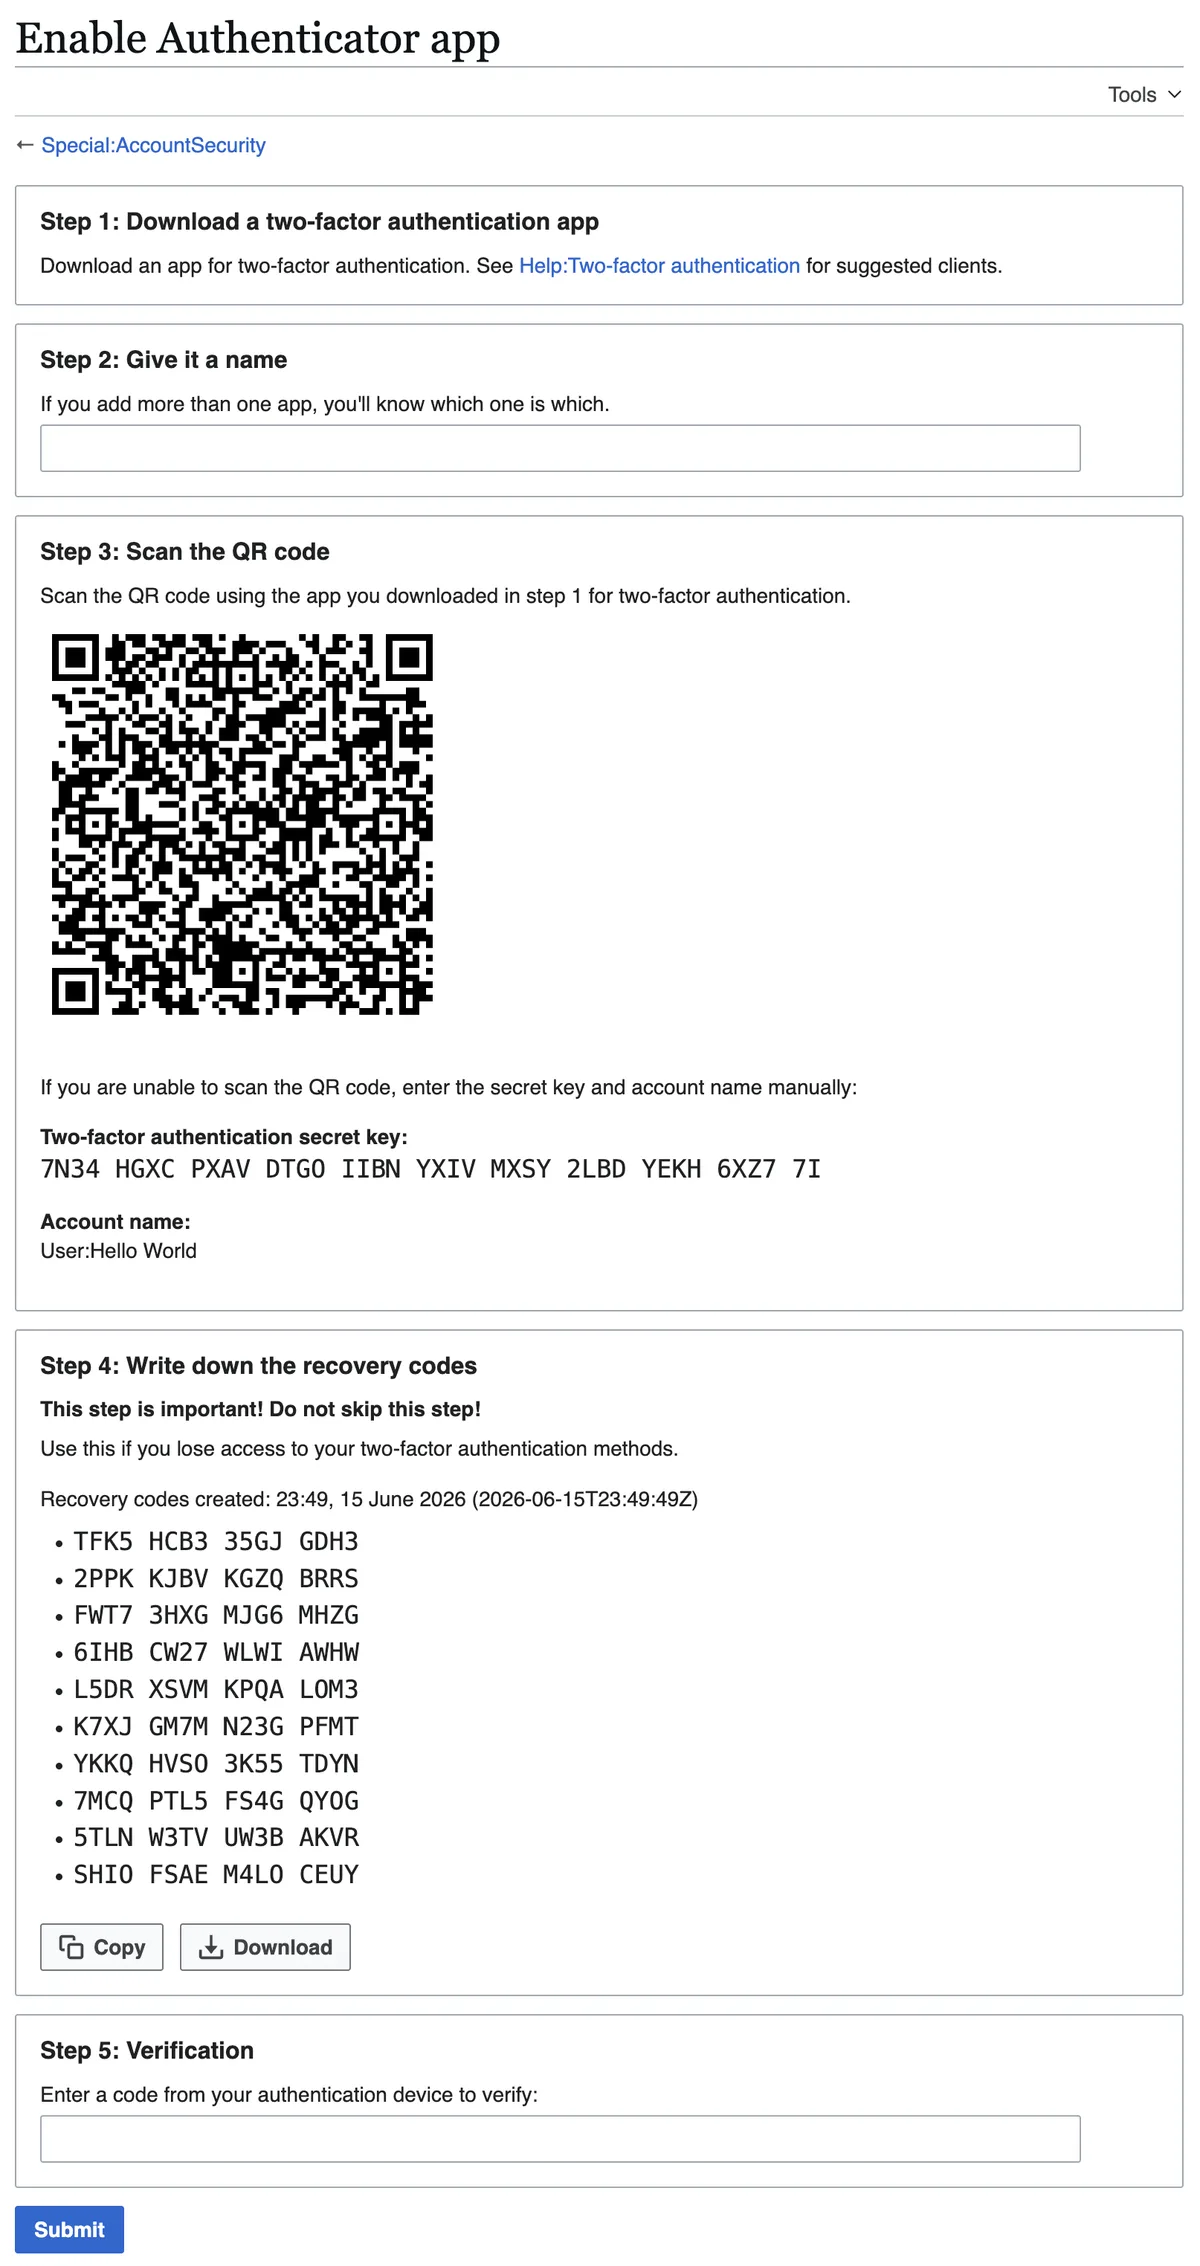
- If you chose an app, the site shows a QR code. Open your authenticator app, choose Add account, and scan it. You will see a six-digit code that refreshes every 30 seconds or so. That is your second factor.
- Enter the current code on the website to confirm the connection works.
- Save your backup codes. The site offers a set of one-time recovery codes. Download them or print them, and store them somewhere safe but not in the same place as your password.
That last step is the one beginners skip. Backup codes are what get you back in if you lose your phone. Without them, recovery can take days of proving your identity to the provider.
How do I turn on 2FA for banking and social accounts?
Banks vary more than any other category. Some offer an authenticator app, some push a prompt to their own mobile app, some rely on text messages only. Open your bank's mobile app and look under Profile, Security, or Login settings. If nothing is offered in the app, check the bank's help pages or call the number on the back of your card and ask what second-factor options exist. Take whatever the bank provides; a text-message code still beats a password alone.
Social platforms follow the same pattern as email. On most of them the path runs through account settings, then Security or Login, then Two-factor authentication. Prefer the app method over SMS when both appear. After enabling it, check the recovery section once: confirm your backup codes are saved and that a second recovery method, such as another email, is current.
If you want the deeper walkthrough for the biggest platforms, our guide on turning on 2FA for the accounts that matter most covers each provider step by step, and there is a dedicated walkthrough for your Google account as well.
What this means: realistic outcomes, not guarantees
Two-factor authentication is not a force field. Account takeover still happens, most often when a person is tricked into approving a login prompt or reading out a code to someone posing as support staff. The realistic outcome is narrower and still worth it: a stolen password, on its own, stops working. That kills the bulk of automated takeover attempts, which is exactly what most attacks on ordinary accounts are. We covered a connected angle in How to turn on two-factor authentication for the accounts that matter most.
Two habits keep the protection honest. First, never share a login code with anyone, including someone who calls you and says they are from your bank or a platform. Real support staff do not ask for it. Second, keep your recovery methods current. If you change phone numbers or replace your phone, update the second factor on your key accounts the same week, and re-save fresh backup codes.
For a broader routine, our monthly personal security checklist folds 2FA upkeep into a short session, and if you want to move from text codes to an app later, the guide on switching from SMS to an authenticator app covers the migration.
Where to go from here
You now know what two-factor authentication is, which accounts earn it first, and the general path to turn it on. Do email today, banking this week, social after that. Save the backup codes every time. Once the basics are in place, the natural next steps are sign-in alerts so you can see logins as they happen, and phishing awareness, because a code handed to a scammer undoes the whole system. Both have full guides on this site. Security is a series of small, boring, effective habits, and this one is the highest-value habit on the list.