Threats tracks live attack activity: ransomware operations, malware families, phishing infrastructure, credential theft and supply chain compromise. Each report explains initial access, movement and persistence, then lists indicators and the sectors under pressure. Written for defenders deciding what to prioritize with limited hours.
A supply chain attack compromises a vendor, update mechanism, or dependency so malicious code rides in through a trusted channel — the defense is fewer dependencies, verified builds, and fast patch…
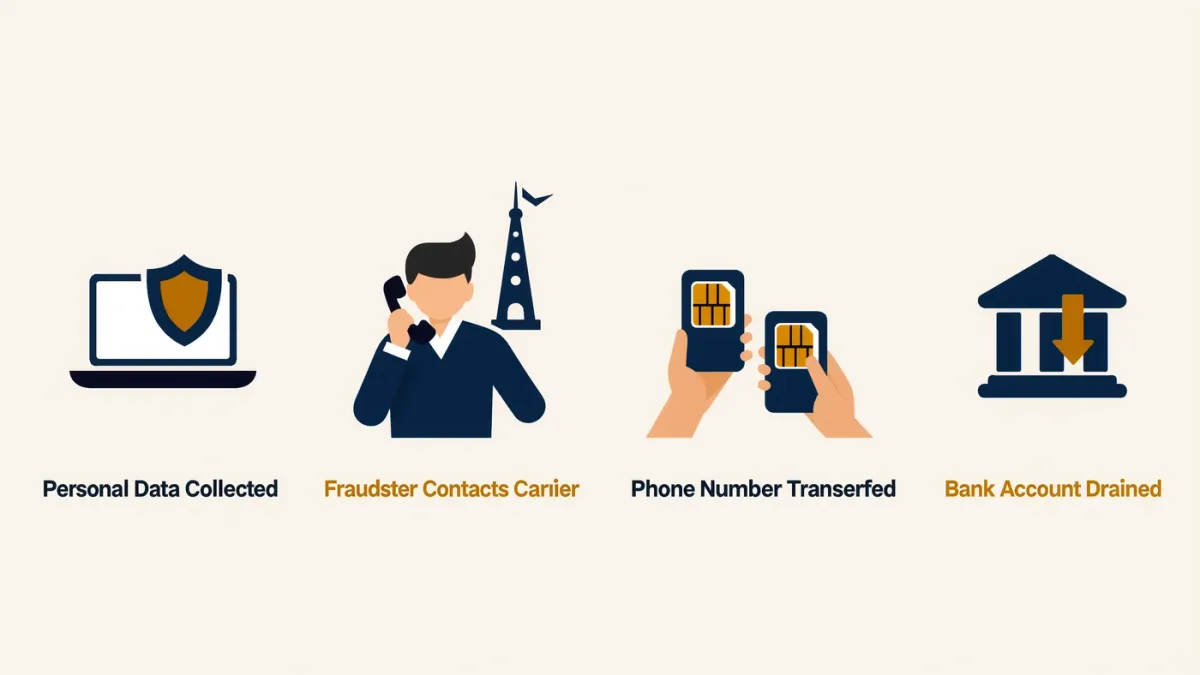
In a SIM swap, a fraudster moves your phone number to a SIM card they control — intercepting your SMS codes and password resets in the process; a carrier port-out PIN and non-SMS two-factor…
Ransomware encrypts your files and demands payment, and modern crews also steal the data first — so the defense that matters most is a backup the attackers cannot reach.